Laravel Packages

Automated Composer Security Audits in Laravel with Warden

Published
Automated Composer Security Audits in Laravel with Warden image

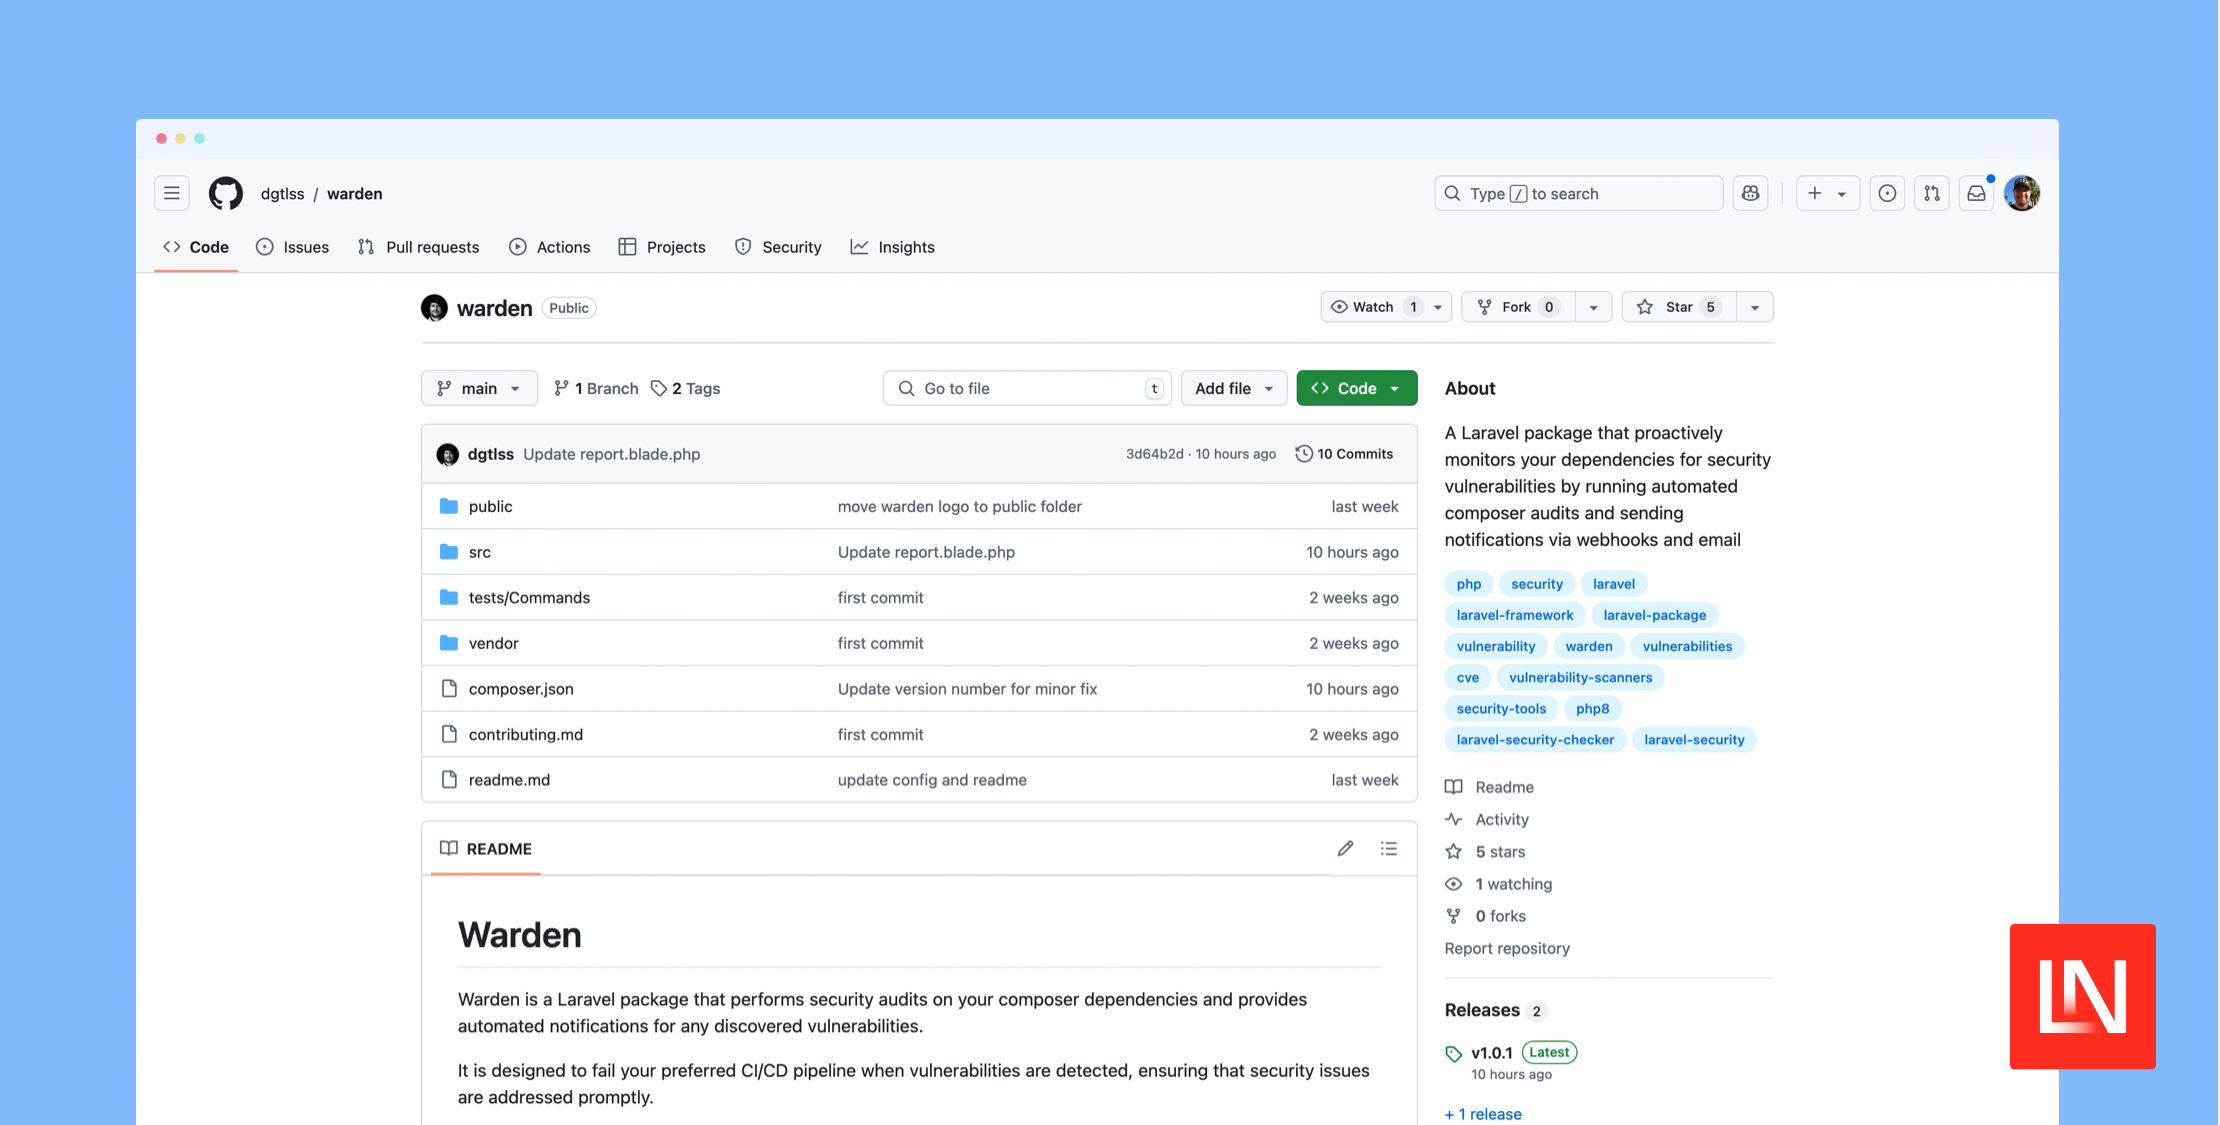
Warden is a Laravel package that performs security audits on your Composer dependencies and provides automated notifications for vulnerabilities. With your CI pipeline automation, Warden can help you promptly identify and address issues.
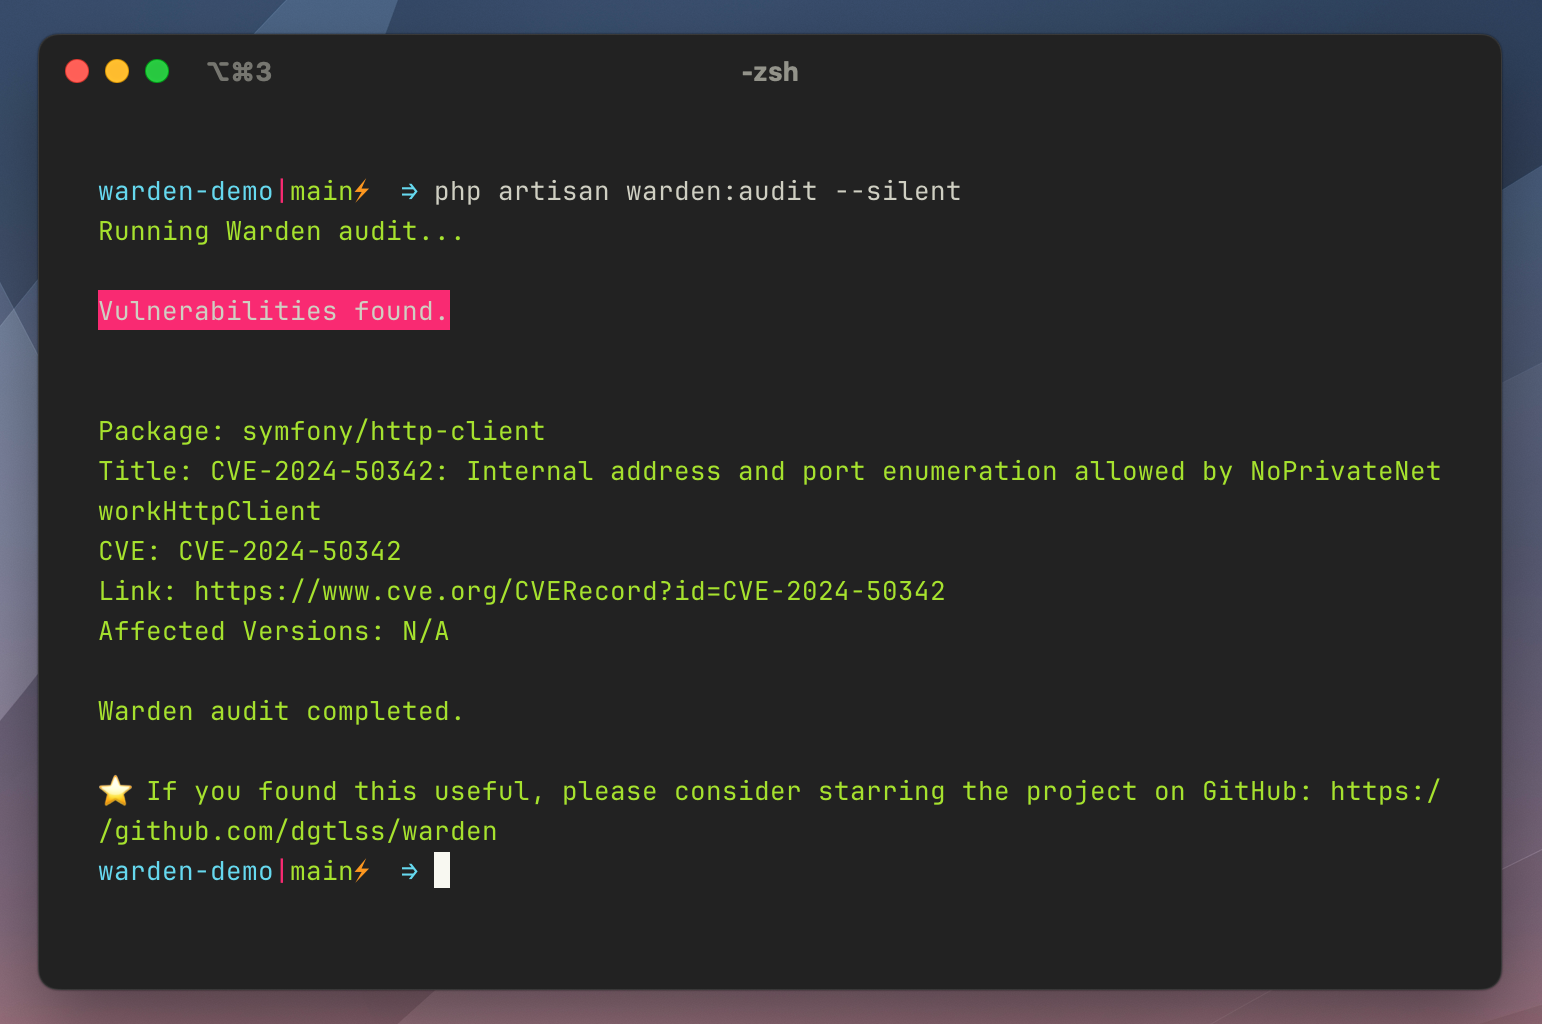
This package supports webhook or email notifications, sending reports with affected packages, affected versions, and more from the composer audit command. All this gets triggered from the warden:audit Artisan command:

php artisan warden:audit
 
# Run without sending notifications
php artisan warden:audit --silent

The documentation includes configuration and setup steps required to install the package, as well as instructions on incorporating it into your CI/CD pipeline. You can learn more about this package, get full installation instructions, and view the source code on GitHub.

Paul Redmond photo

Staff writer at Laravel News. Full stack web developer and author.

Sponsored

masteringlaravel logo
Laravel Code Review

Get expert guidance in a few days with a Laravel code review

Visit Laravel Code Review

The latest

View all →
Volker Dusch on the PHP RCE Vulnerabilities and Disclosure image

Volker Dusch on the PHP RCE Vulnerabilities and Disclosure

Read article
Decide with Jev: Turn AI Answers into Decisions with PHP Rules image

Decide with Jev: Turn AI Answers into Decisions with PHP Rules

Read article
Skuul: Open-Source School Management Built on Laravel image

Skuul: Open-Source School Management Built on Laravel

Read article
Laravel Read Replicas: Prevent Stale Reads After a Write image

Laravel Read Replicas: Prevent Stale Reads After a Write

Read article
Screenshot: Capture Images and PDFs with PHP and Laravel image

Screenshot: Capture Images and PDFs with PHP and Laravel

Read article
Reset Sticky Database Connections Between Laravel Queue Jobs image

Reset Sticky Database Connections Between Laravel Queue Jobs

Read article